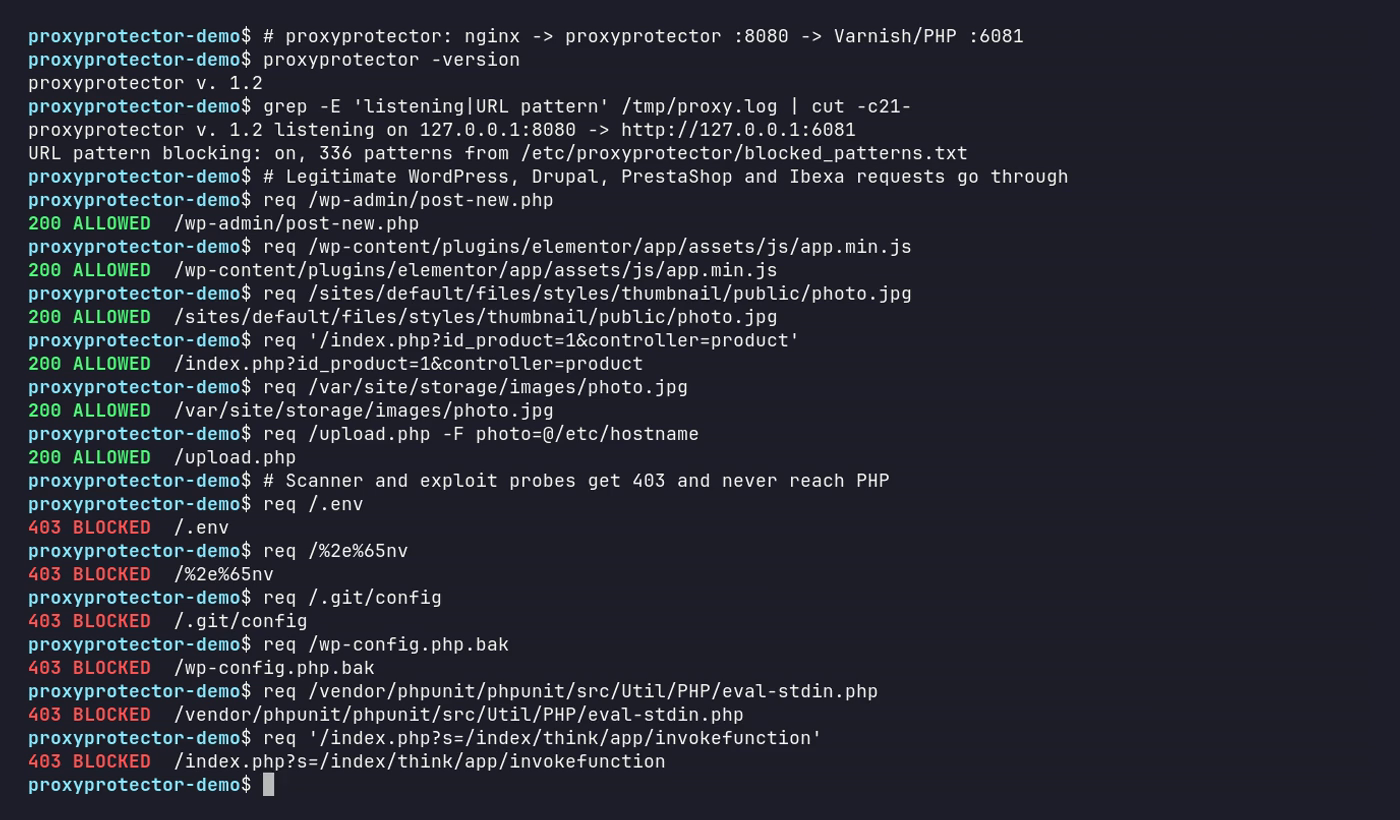
Watch it in action: scanner probes get 403, real WordPress, Drupal, PrestaShop and Ibexa traffic goes through.
Proxy Protector
door Carles Mateo
 Linux
CVE-2026-109618
CVE-2026-109619
exploit
Firewal
IP
PHP2Shell
Security
Proxy Protector it's a protector of your web connections and mitigates PHP2Shell in old configurations, also has a built-in WAF (Web Application Firewall) to protect from common attacks
Proxy Protector
Stop PHP2Shell at the door — without touching your PHP code.
By Carles Mateo
▶
The problem
PHP2Shell (CVE-2026-109618 / CVE-2026-109619) lets attackers turn crafted requests into remote code execution on vulnerable PHP versions, and exploit tooling is already in the wild. The real fix is upgrading PHP to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 - but on real servers that can take days or weeks: legacy applications, frozen platforms, change windows, customers who can't be moved yet, some mitigations can be applied.
nginx and Varnish can’t properly filter these attacks: they don’t parse multipart bodies the way PHP does, and that gap is exactly what the exploits rely on.
The solution
Putting your legacy server behind Cloudflare (and not allowing direct connections) is being told to protect from PHP2Shell attacks. Other CDNs may work too.
Configuring some parameters in php.ini may help to mitigate, those are:
session.upload_progress.enabled = 0
session.use_strict_mode = 1
Also having a lot of memory for the PHP requests.
And disabling in php.ini execution functions, for instance:
disable_functions = exec,shell_exec,system,passthru,proc_open,popen,proc_close,proc_get_status,proc_terminate,proc_nice,putenv,dl,symlink,link,posix_kill,posix_setuid,posix_setgid,posix_setsid,posix_setpgid,posix_mkfifo,pcntl_exec,pcntl_alarm,pcntl_fork,pcntl_waitpid,pcntl_wait,pcntl_wifexited,pcntl_wifstopped,pcntl_wifsignaled,pcntl_wifcontinued,pcntl_wexitstatus,pcntl_wtermsig,pcntl_wstopsig,pcntl_signal,pcntl_signal_get_handler,pcntl_signal_dispatch,pcntl_get_last_error,pcntl_strerror,pcntl_sigprocmask,pcntl_sigwaitinfo,pcntl_sigtimedwait,pcntl_getpriority,pcntl_setpriority,pcntl_async_signals,pcntl_unshare,imap_open,phpinfo
PHP-FPM is told to be more resilient than Apache with modphp.
Adding Proxy Protector adds an additional layer of protection and blocks another great deal of the PHP2Shell attacks hopefully buying you some time. (to definitive solve the vulnerability you need to update PHP to a supported version ASAP on your legacy server)
- Shuts the door on scanners. 336 signatures from PHP Firewall, built from real attack traffic, return 403 for probes for leaked secrets (`/.env`, `/.git/`, config backups), web shells, database dumps and exploit URLs. Patterns that would hit legitimate WordPress, Drupal, PrestaShop or Ibexa URLs are excluded out of the box, and the list is a plain text file you can extend. (you can disable this in the config file)
- Re-encodes every upload. Multipart bodies are fully parsed and rebuilt from scratch, so PHP receives exactly what the proxy inspected. Parser-differential tricks — odd boundaries, duplicated headers, trailing junk — simply disappear.
- Blocks the upload-progress delivery path. The `PHP_SESSION_UPLOAD_PROGRESS` field is rejected.
- Validates session cookies. Malformed, oversized or duplicated `PHPSESSID` cookies are denied.
- Uploads only where you allow them. Multipart requests are accepted only on the endpoints you list. If you don't need uploads, the site will be much more safe.
- Per-endpoint size limits, enforced up front. Chunked bodies are read completely before forwarding, so limits apply before the backend sees a single byte.
- Handles big uploads. 2 GB uploads are spooled to disk, not memory.
- Clear logs. Every rejection is logged with status, client IP, method, path and reason.
Easy to deploy
- One static binary, no dependencies, no runtime to install.
- Simple config file, or command line flags — or both.
- Ready-made systemd unit with hardening options.
- Up and running in about five minutes; no change to your PHP application.
Supported platforms
Architecture, runs on:
Linux x86-64 (Intel/AMD): Tested on Ubuntu 26.04 LTS, Ubuntu 24.04 LTS, Debian 13, Debian 12
Linux ARM64 (AWS Graviton, Ampere, Raspberry Pi 4/5): Tested on Debian 13, Ubuntu 24.04 LTS
Works with nginx + Varnish + PHP-FPM/Apache stacks, or nginx directly in front of a PHP web server.
What’s in the download
- `proxyprotector-linux-amd64` and `proxyprotector-linux-arm64` binaries
- `proxyprotector.conf.example` — fully commented configuration
- `blocked_patterns.txt` — scanner and exploit URL signatures, editable
- `proxyprotector.service` — systemd unit
- `SHA256SUMS` — checksums of the binaries
- User guide and changelog
Configuration at a glance
The default configuration:
| Listen address / port | `127.0.0.1:8080` |
| Backend (Varnish or PHP) | `127.0.0.1:6081` |
| Max body, normal requests | 8 MB |
| Max body, upload endpoints | 2 GB |
| Max multipart parts | 200 |
| Max Cookie header | 4096 bytes |
| Upload endpoints | `/upload.php` |
| Session ID format | `^[A-Za-z0-9,-]{22,64}$` |
| Upload-progress field name | `PHP_SESSION_UPLOAD_PROGRESS` |
| Block scanner / exploit URLs | On (`block_url_patterns = 1`) |
Honest about its limits
proxyprotector is a mitigation, not a fix. The underlying flaw is in PHP’s out-of-memory handling, and a request that stays within your limits can still, in some cases, reach it. proxyprotector blocks the known delivery paths and buys you time to upgrade safely. Upgrade PHP as soon as you can — after that you can keep proxyprotector as an extra layer of defence or retire it.
Even for systems with modern PHP version, patched up to date, Proxy Protector it's a great protective security tool.
FAQ
Do I need to change my PHP application?
No. Point nginx’s `proxy_pass` at proxyprotector and list your upload endpoints.
Does it handle HTTPS?
nginx (or another software) keeps terminating TLS; proxyprotector runs behind it on localhost and sees all traffic, HTTP and HTTPS.
Will it slow my site down?
Normal requests are forwarded with negligible overhead. Uploads are rebuilt in a single streaming pass to a temp file.
Does it run on Windows?
Server binaries are provided for Linux only.
Will the URL blocking break my CMS?
The shipped list is tested against legitimate URLs of WordPress, Drupal, PrestaShop and Ibexa. If your own application uses a blocked URL, you can disable it with one edit to the patterns file, or disabling the WAF in the config file.
Can I run it without Varnish?
Yes. Set `destination_server_host` / `destination_server_port` to your PHP web server.
Pricing and licence
- Licence: Per server
- Updates: Free for the next 6 months after purchase
- Support: Only by email
If you need online help setting Proxy Protector, we can help you at a rate/hour.
Bijlagen
- Proxy Protector Intel 64 bits and ARM 64 bits v. 1.2 (5.0 MB)
€120